





de Recherche et d’Innovation
en Cybersécurité et Société
Bienvenu
If needed, this section can contain some or all of the following:
- A large, engaging image of the university, department, or an abstract representation of the academic field can set a professional and inspiring tone.
- A brief welcome message or introduction that explains what visitors will find on the page. This could be a short paragraph detailing the purpose of the page, such as highlighting the academic and research achievements of the faculty.
- Key facts, achievements or statistics about the professor or department. For instance, number of published papers, years of experience, key projects, or awards won.
- Interactive timeline that highlights major milestones, such as significant publications, awards, and other achievements.
- A short video where the professor introduces themselves and talk about their work and interests providing a personal touch, and making the page more engaging and approachable.
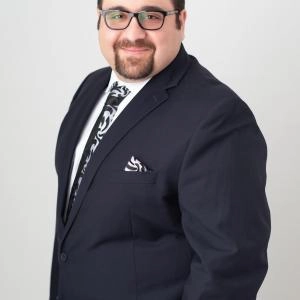
Hamed Motaghi
Professeur
Université du Québec en Outaouais (UQO)
Département des sciences administratives
Hamed Motaghi détient depuis 2015 un Ph.D. en administration des affaires de l’UQAM, spécialisé en gestion de la technologie. Professeur régulier à l’UQO depuis 2016, et détenteur d’un financement du CRSH, il apporte à notre équipe son expertise sur la créativité et l’innovation dans les organisations, surtout face aux défis de cybersécurité et vie privée, et les compétences en cybersécurité des populations immigrantes et réfugiées. Il dirigera l’axe 2 « Employé.e.s et compétences ».
Productions incluses dans la recherche:
AUT (Autres), BRE (Brevet), CAC (Publications arbitrées dans des actes de colloque), CNA (Communication non arbitrée), COC (Contribution à un ouvrage collectif), COF (Communication arbitrée), CRE, GRO, LIV (Livre), RAC (Revue avec comité de lecture), RAP (Rapport de recherche), RSC (Revue sans comité de lecture).
Année : 1975 à 2026
Publications sélectionnées
2026 |
Irikefe, P. O.; Falahat, M.; Zainudin, A. D.; Motaghi, H. Dans: Journal of Cleaner Production, vol. 574, 2026, ISSN: 09596526 (ISSN). @article{irikefeEntrepreneurialLeadershipResource2026,Small and medium enterprises (SMEs) are central to employment and value creation, yet pressures from sustainability transition expose endemic financing frictions and uneven digital readiness (DR), particularly in emerging markets. This study examines how SME capabilities viz.: entrepreneurial leadership (EL) and resource management efficiency (RME) associate with triple-bottom-line (TBL) sustainability across economic (ECOS), environmental (ENVS), and social (SOCS) pillars, whether firm-level financial inclusion (FI) statistically mediates capability-to-TBL associations, and whether DR conditions these associations. Using survey data from 429 Malaysian SMEs, we apply a sequential analytics design: Partial Least Square-Structural Equation Modelling to test direct, mediated, and interaction effects; followed by Necessary Condition Analysis (NCA) and Importance-Performance Map Analysis in the bid to identify bottlenecks and practical priorities. Results show that EL is positively associated with ECOS, ENVS, and SOCS; whereas RME is strongly positively associated with ECOS and ENVS but is not significant for SOCS. FI is TBL pillar-asymmetric: it bolsters ENVS and SOCS but exhibits a negative effect on ECOS, and the mediated effects through FI mirror the pattern. DR significantly strengthens the FI to TBL pathways, yet conditional indirect effects indicate that high DR can neutralise FI's economic drag without reliably improving ECOS. NCA sharpens the conclusion: high ECOS is unattainable without RME, while high ENVS and SOCS require EL-RME-FI jointly; DR is not a robust necessity condition. Practically, SMEs should tighten efficiency routines first, mobilise leadership for adoption, channel finance through verified upgrading milestones and invest in DR only where it improves monitoring, traceability and compliance. Copyright © 2026. Published by Elsevier Ltd. |
2025 |
Noor, A. F. Mohamed; Moghavvemi, S.; Tajudeen, F. P.; Motaghi, H.; Salehi, A. Cybersecurity Readiness: A Review via Dynamic Capabilities Article d'actes Dans: M., Myers; R.A., Alias; W.F., Boh (Ed.): Pac. Asia Conf. Inf. Syst., Association for Information Systems, 2025, ISBN: 26896354 (ISSN). @inproceedings{mohamed_noor_cybersecurity_2025,Understanding the factors influencing cybersecurity readiness is crucial for strategic investment in cyber capabilities. However, there is a gap in applying Dynamic Capabilities (DC) theory, which focuses on organizational agility in adapting to changing environments. This study fills this gap by using DC theory to analyze and categorize existing literature, offering a framework to classify cybersecurity readiness factors across different stages. This approach enhances our understanding of how organizations maintain a competitive edge amidst evolving cyber threats. The study addresses the following research question: What are the key factors influencing cybersecurity readiness in organizations, as discussed in literature from 2014 to 2023? Utilizing a thematic review with Atlas.ti 23, it examines literature from 2014 to 2023, providing a broad perspective on relevant factors. By applying DC theory, this research offers valuable insights for academics, organizations, and policymakers, aiding in strategy development and informed policymaking. © 2025, Association for Information Systems. All rights reserved. |
Nosrati, S.; Motaghi, H. The AI Complacency Model: Integrating Bounded Rationality and Information Processing Article d'actes Dans: Am. Conf. Inf. Syst., AMCIS, p. 4590–4599, Association for Information Systems, 2025, ISBN: 979-833132774-3 (ISBN). @inproceedings{nosrati_ai_2025,This study addresses a critical gap in understanding why users exhibit reduced oversight when interacting with generative AI systems despite their known limitations. While existing research documents AI errors across domains, theoretical frameworks explaining the underlying psychological mechanisms remain underdeveloped. We propose a comprehensive model of AI complacency that extends beyond traditional automation complacency theories by integrating bounded rationality constraints with dual-process information processing models. Our framework demonstrates how Perceived AI Reliability triggers a shift from systematic to heuristic information processing, subsequently reducing vigilance and impairing task performance. The relationship between Perceived AI Reliability and information processing is moderated by three key factors derived from bounded rationality theory: knowledge limitations, cognitive processing capabilities, and time constraints. The proposed conceptual model of this study contributes to the literature by identifying unique psychological mechanisms underlying AI complacency, explaining the processing shifts in human-AI interaction, positioning vigilance as a critical mediating mechanism, and introducing the Vigilance-Reliability Matrix as a diagnostic tool for identifying different interaction patterns. This framework offers both theoretical insights and practical guidance for maintaining appropriate human oversight as AI systems become increasingly sophisticated and widespread across domains. Copyright © 2025 by Association for Information Systems (AIS). All rights reserved. |
Some Heading
If needed, this section can contain some or all of the following:
- Recent news, updates, or upcoming events related to the professor or their department, such as guest lectures, seminars, and conferences.
- Social media feed.
- A quote from the professor about their philosophy on education and research or a testimonial from a peer or student adding a personal and inspirational element to the page, placing this information just above the share icons can give visitors current and relevant reasons to engage and share.
- Call to Action to attend or participate in some even.
- Contact Form
- Subscribe form